Managed SOC / NOC Services
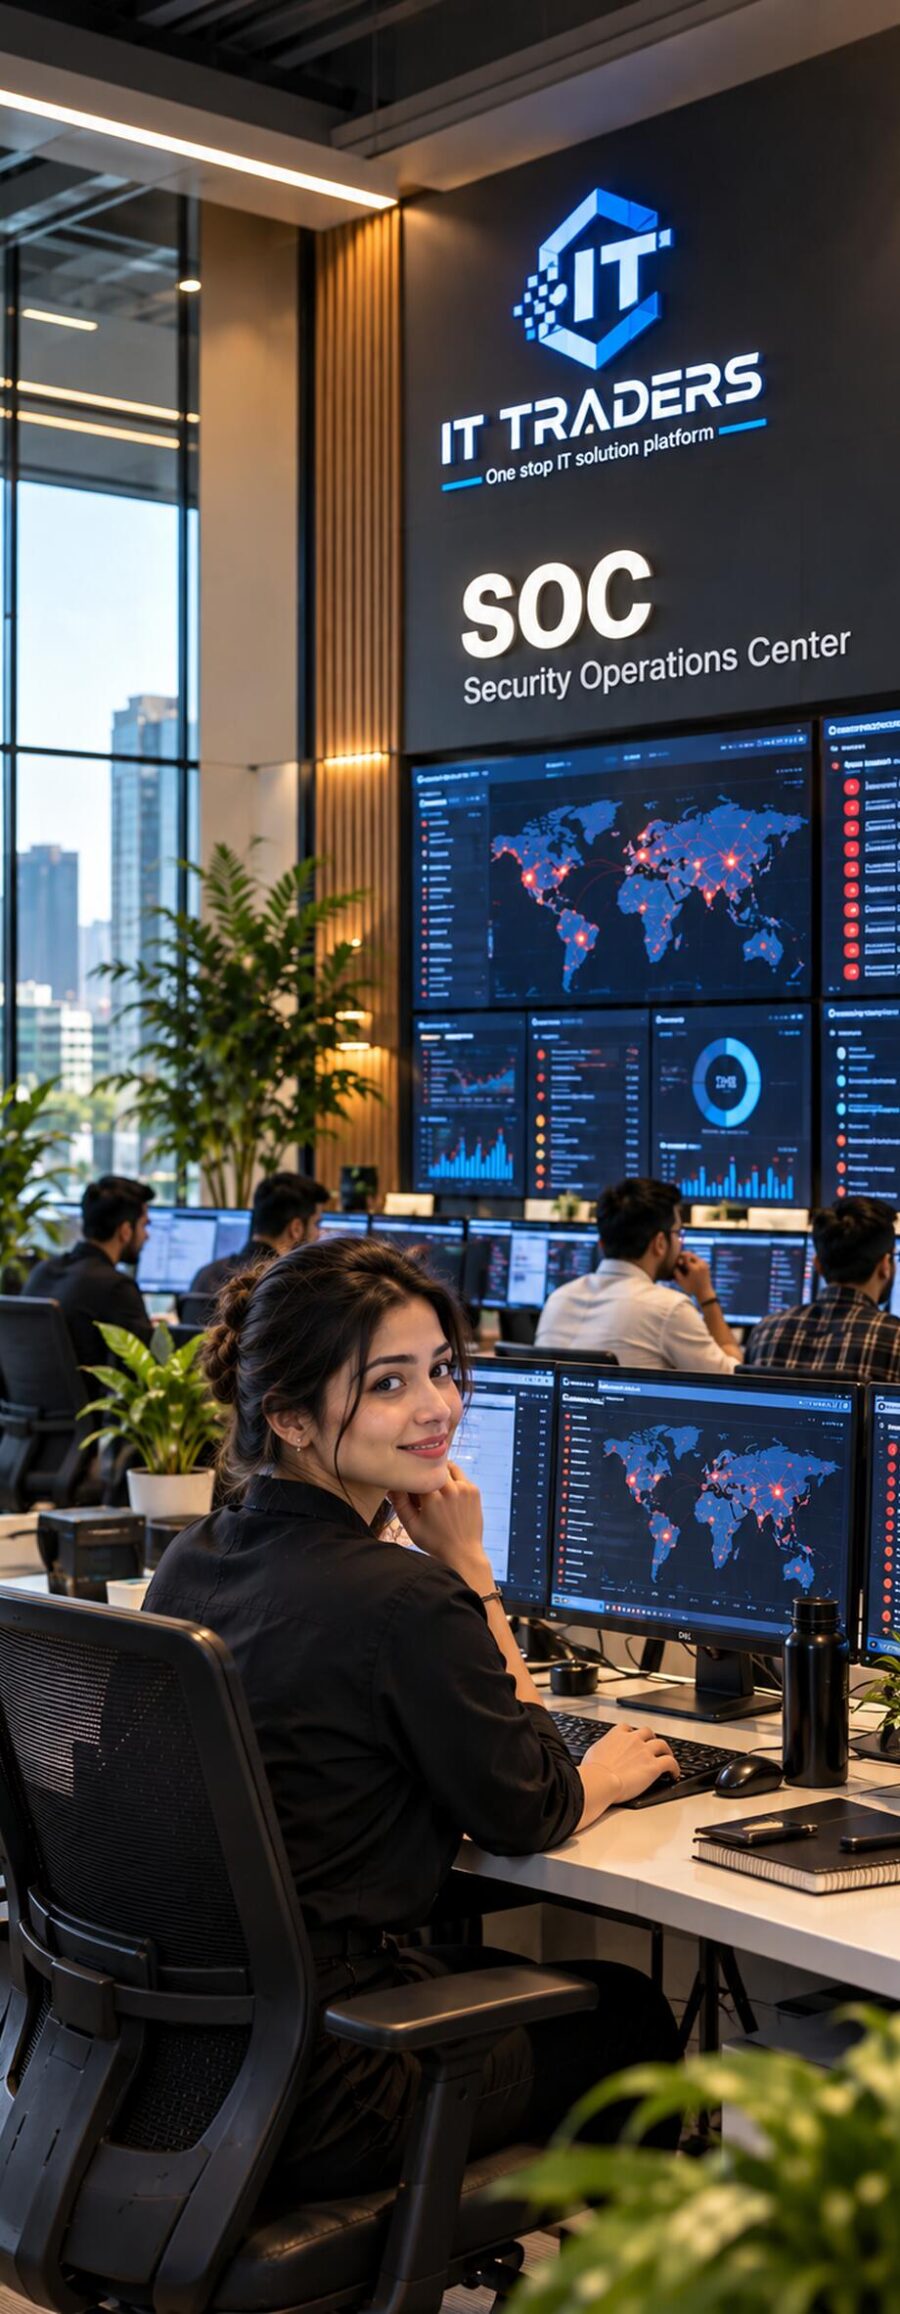
24×7 Security & Network Operations Centre — threat monitoring, SIEM analytics and incident response.
What We Deliver
24/7 Security Monitoring
Round-the-clock monitoring of firewalls, endpoints, servers and cloud.
SIEM & Log Correlation
Centralised logs and correlated alerts to spot real threats fast.
Network Operations (NOC)
Uptime, bandwidth and device health monitoring with proactive fixes.
Incident Response
Triage, containment and escalation following clear runbooks.
Threat Hunting
Proactive hunts for hidden and dormant threats across your environment.
Monthly Reporting
Clear security and uptime reports with actionable recommendations.
SOC as a Service Without Building Your Own Security Team
Hiring and retaining round-the-clock security analysts is out of reach for most mid-sized companies. Our managed SOC services give you a 24/7 security operations center and network operations center as one service: we collect logs from Sophos, Fortinet, Palo Alto, CrowdStrike and Microsoft Defender, correlate them in a SIEM, investigate alerts and respond — so real threats are contained quickly and your team only hears about what matters.
Onboarding starts with mapping your critical servers, firewalls, endpoints and cloud accounts, then connecting their logs and setting alert rules that match your business. You receive monthly SOC reports covering incidents, response times and recommendations, and our analysts stay on call for escalations around the clock, including weekends and holidays.
Supported Security & Monitoring Platforms
Security and network platforms our SOC/NOC monitors and manages around the clock.
| Brand | Target Use Case | Key Highlights | Sourcing & Support |
|---|---|---|---|
 FortiGate & FortiAnalyzer |
Network Security Monitoring | Centralised logs, threat analytics, automated alerts | 24/7 monitoring, incident response |
 Central & MDR |
Endpoint & Firewall Monitoring | Synchronized security, managed threat response | Alert triage, response, reporting |
 Falcon |
Endpoint Threat Detection | Real-time endpoint telemetry and threat intelligence | Threat hunting, containment |
 Defender & Sentinel |
Microsoft 365 & Azure Environments | Cloud-native SIEM and XDR correlation | Monitoring, correlation, response |
|
Enterprise Perimeter | Next-gen firewall logs and threat prevention | Policy monitoring, incident handling |
Supported Brands
Our 4-Step Managed SOC / NOC Onboarding Methodology
How we bring your security and network operations under 24/7 expert watch.
Environment Discovery
We map firewalls, endpoints, servers, cloud and network devices to be monitored.
Integration & Baselining
Log sources connected to SIEM, alert rules tuned and normal behaviour baselined.
24/7 Monitoring & Triage
Round-the-clock analysts watch alerts, investigate incidents and escalate per runbook.
Response, Reporting & Improvement
Incident containment, monthly reports and continuous rule improvement.
Key Business Benefits & Value Proposition
Why Businesses Choose IT Traders for Managed SOC / NOC
- 24/7 Eyes on Your Network: Threats and outages are caught at night and on weekends, not on Monday morning.
- No In-House SOC Needed: Get a full security and network operations team without hiring one.
- Faster Detection & Response: Correlated alerts and clear runbooks shorten time to contain incidents.
- Less Downtime: Network issues are spotted and fixed before users notice.
- Clear Monthly Reporting: Understand your security posture with simple, actionable reports.
Solutions by Industry
The same toolset, tuned to the compliance, scale and budget realities of each sector we serve.
Manufacturing
Plant-floor networks, OT security and surveillance built for 24×7 production environments
Explore this industry
BFSI
RBI/IRDAI-aligned infrastructure, security and disaster recovery for banks, NBFCs and insurers
Explore this industry
Healthcare
Secure, always-on infrastructure for hospitals, diagnostics chains and clinics
Explore this industry
IT / ITeS
Scalable infrastructure, leased lines and security for software companies, BPOs and GCCs
Explore this industry
Retail
Multi-branch networking, POS infrastructure and surveillance for stores and chains
Explore this industry
Education
Campus WiFi, smart classrooms and Microsoft 365 Education for schools, colleges and universities
Explore this industryNeed Managed SOC / NOC Services?
Get a genuine, competitive quote from our experts within 4 business hours.
Our Technology Partners
We Have the Best Partners to Drive Your Business
Our longstanding partnership with leading enterprise IT solution platforms enables us to deliver curated digital transformation services.